SonicWall SSLVPN SAML bypass hits KEV: MFA you enforced, skipped with the other password
you bolted SAML and MFA onto the SonicWall SSL VPN. good sloth. but if the same user still has a second way to log in, CVE-2026-19868 says the firewall may let that second way walk right past the SAML door. SonicWall says it investigated a report of potential exploitation, and CISA put it on KEV on November 6. the sloth is moving at full speed, which is to say, reading the firmware number twice.
the exact condition, no inflation
- SAML has to be on for SSLVPN logins. SonicWall’s words: the vulnerability “ONLY impacts the SonicOS SSLVPN interface or service if SAML is enabled for SSLVPN logins.” no SAML on SSLVPN, no CVE-2026-19868 on that interface.
- the attacker needs valid credentials. specifically, valid credentials for an alternate authentication method. this is not a credential-free takeover. it is “your MFA policy was not the only door.” SonicWall’s advisory does not name which alternate methods, so check every non-SAML way a user can authenticate on your box.
- why it still matters: stolen and reused VPN passwords are cheap. the whole point of forcing SAML plus MFA is that a leaked password alone should not be enough. this bug is about that guarantee.
scores, and who gave them
- SonicWall (vendor): CVSS 3.1 7.1,
AV:N/AC:H/PR:L/UI:N/S:C/C:H/I:L/A:N. note PR:L, matching the credential requirement. - CISA ADP enrichment in the CVE record: CVSS 3.1 7.5,
AV:N/AC:H/PR:N/UI:N/S:C/C:H/I:L/A:N, SSVC exploitation “active”, automatable “no”, technical impact “partial”. NVD had not published its own score at the time of writing. - CWE-308, use of single-factor authentication. credit: Ryan Harris of The Electronic Office, per SonicWall.
affected and fixed (from SNWLID-2026-0014)
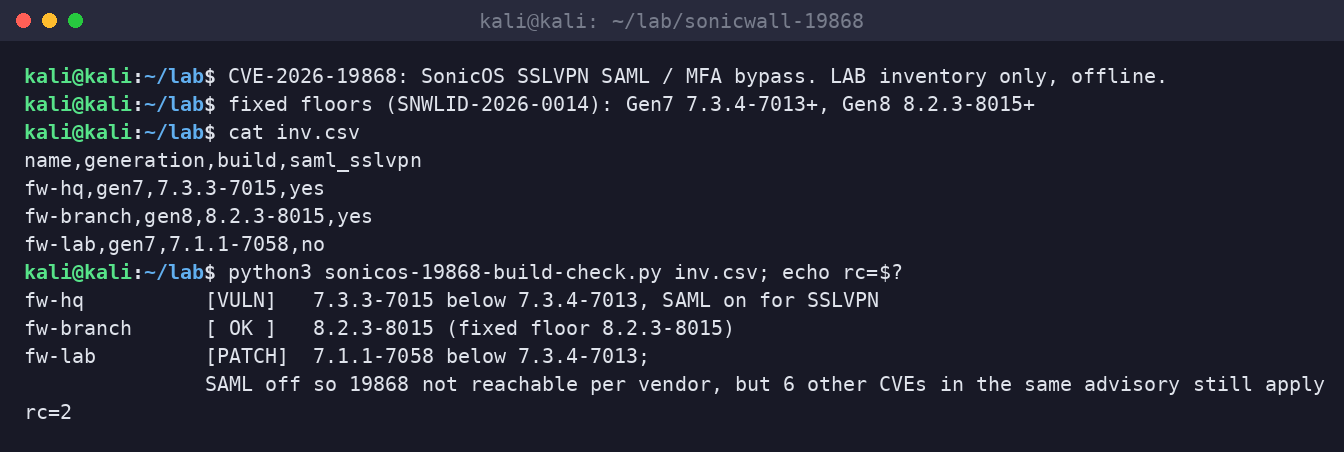
- Gen7 hardware (TZ 270 through TZ 670, NSa 2700 through 6700, NSsp 10700 through 15700) and Gen7 NSv 270, 470, 870 on ESX, KVM, Hyper-V, AWS and Azure: 7.3.3-7015 and older affected, fixed in 7.3.4-7013 and higher.
- Gen8 hardware (TZ 80 through TZ 680, NSa 2800 through 5800) and Gen8 NSv XS, S, M, L: 8.2.2-8015 and older affected, fixed in 8.2.3-8015 and higher.
- workaround: SonicWall lists none. upgrading is the fix.
- check the exact model list in the advisory against each appliance, virtual ones included.
the other six in the same advisory
same firmware, same upgrade. none of these carry SonicWall’s exploitation note, and only CVE-2026-19868 is on KEV:
- CVE-2026-107155 (permissive cross-domain policy) and CVE-2026-107154 (session validation, reliance on IP address) in the management interface, both vendor CVSS 8.8, “in specific conditions” letting a remote unauthenticated attacker perform unauthorized operations.
- CVE-2026-82308, pre-authentication heap overflow in the SSL-VPN service, application-level denial of service, 7.5.
- CVE-2026-77708 and CVE-2026-77709 in the TACACS+ authentication client, denial of service in specific conditions.
- CVE-2026-19703, weak password hashing.
what to do today
- inventory. model, generation and running build for every firewall, including NSv. a pinned build on the branch office box counts.
- upgrade to 7.3.4-7013+ (Gen7) or 8.2.3-8015+ (Gen8), then confirm the running build actually moved.
- until it moves, shrink the alternate paths. find which accounts can still sign in to SSLVPN without SAML and remove or disable the ones that do not need it. this is hygiene, not a vendor-listed workaround, so do not treat it as a fix.
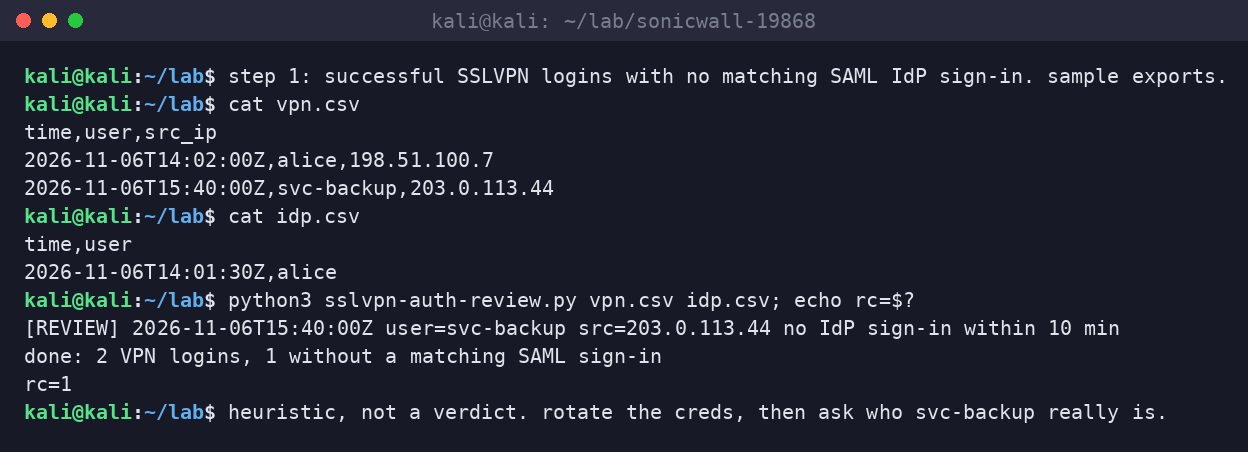
- review logins. any successful SSLVPN login that your identity provider never saw a matching SAML sign-in for deserves a look. rotate passwords for anyone who shows up there.
download the Kali defensive checks
sonicwall-19868-defensive-check.zip contains two offline Python scripts. sonicos-19868-build-check.py reads an inventory CSV you export (name, generation, build, SAML on for SSLVPN) and flags builds below 7.3.4-7013 or 8.2.3-8015. sslvpn-auth-review.py compares successful SSLVPN logins you export against your SAML IdP sign-ins. neither touches a firewall, neither needs credentials, and neither proves or disproves compromise on its own. log column names vary by export, so map them first.
sloth take
MFA is a policy, and a policy is only as strong as the weakest login path that skips it. this bug is the firewall forgetting which door it promised to guard. patch the firmware, then go find out how many of your “SAML only” users still have a second password living in a config page nobody opened since 2022. the sloth is not judging. ok, the sloth is judging a little.
sources
- SonicWall PSIRT, SNWLID-2026-0014, “SonicWall SonicOS Affected By Multiple Vulnerabilities” (November 6, 2026)
- CVE record CVE-2026-19868 (SonicWall CNA, published November 6, 2026), with CISA ADP CVSS and SSVC
- CISA KEV entry (added November 6, 2026, due November 20, 2026)
- NVD CVE-2026-19868