Tracecat Compose SAML signing defaults: new CVE record, configuration-specific risk
A blank value is not always a safe default. The CVE-2026-58490 record was published on November 6, 2026. Tracecat’s underlying advisory is dated July 13, 2026. This is newly catalogued CVE coverage, not a claim of a newly discovered November zero-day.
The affected configuration
The CNA identifies versions from 0.37.0 up to, but excluding, 1.0.0-beta.49. The vendor narrows the problem to affected Docker Compose deployments with SAML enabled and both SAML_SIGNED_ASSERTIONS and SAML_SIGNED_RESPONSES unset, empty or false under the affected deployment defaults. Empty rendered values override secure application defaults and can disable both signature requirements.
The consequence can be a session for an existing Tracecat user, potentially including an existing superadmin. It does not automatically create users where SAML user creation is disabled. Default Fargate and Helm/Kubernetes deployments are excluded by the vendor; do not extend that statement to every customized deployment.
Fix and severity
The vendor identifies 1.0.0-beta.49 as fixed and recommends setting both SAML signing requirements explicitly to true, along with upgrading. The GitHub_M CNA record assigns CVSS 3.1 9.8, consistent with the vector shown in the vendor advisory. No exploitation-in-the-wild claim is made here.
Defensive response
Review the effective Compose environment using your normal deployment controls. Confirm SAML_SIGNED_ASSERTIONS=true and SAML_SIGNED_RESPONSES=true, then redeploy through the approved change process and verify effective settings. Protect configuration output because full environment dumps may contain credentials. Do not paste complete environment dumps into tickets or public chats.
The attached optional checker only inspects those two keys in an operator-supplied dotenv file. It makes no network requests or changes and cannot verify the running container, version, SAML enablement or compromise status. No forged assertion or login attack is supplied. The sloth verdict: explicit signing requirements beat comforting assumptions.
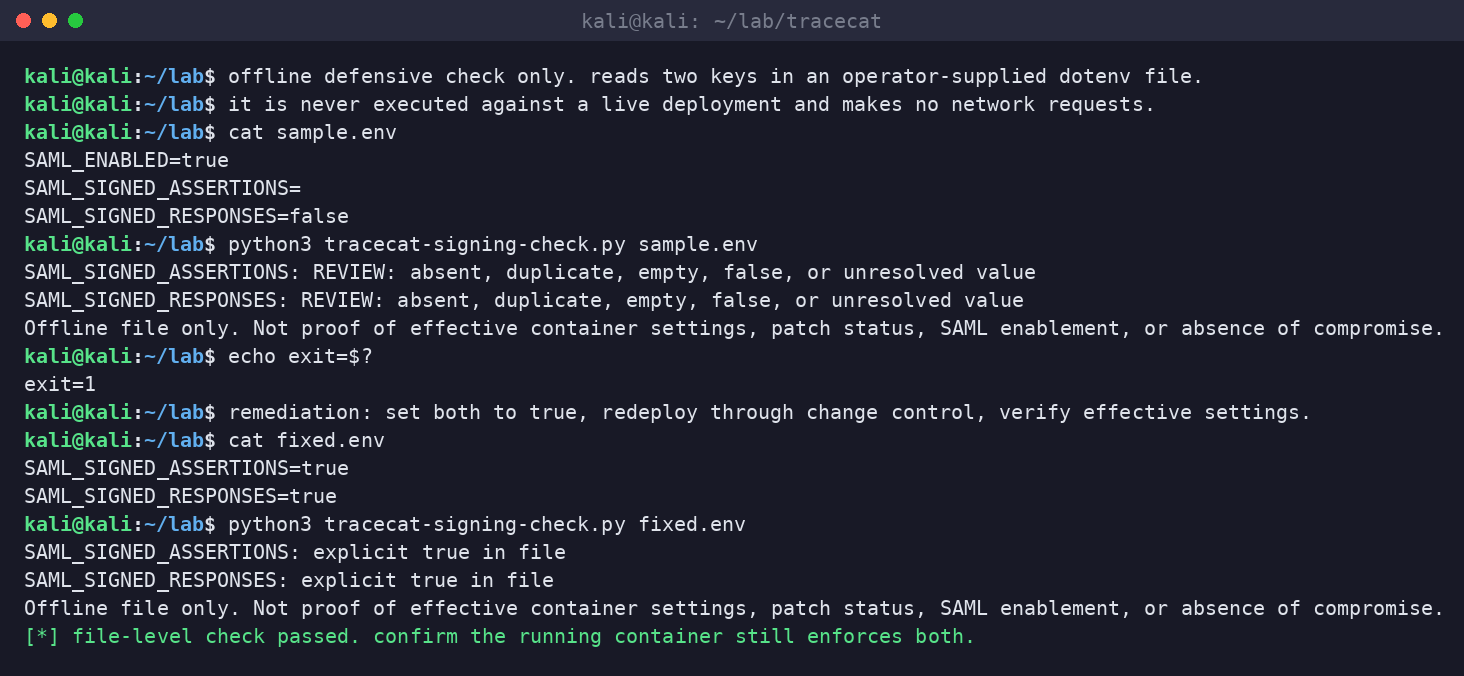
Optional defensive checker. The read-only dotenv checker is available as a download: tracecat-defensive-check.zip. It inspects only SAML_SIGNED_ASSERTIONS and SAML_SIGNED_RESPONSES in an operator-supplied dotenv file, is never executed against a live deployment, and is not a substitute for verifying effective settings.